
Conformidade
8 PUBLICAÇÕES
Ameaças e defesa
DMARC policy: how to move from p=none to p=reject without losing real email
A DMARC record at p=none satisfies Gmail, Yahoo and Outlook, but it stops nobody spoofing your domain. A staged plan to reach p=reject, with the records to publish at each step.
 Ilyas Esmail
Estratégia de Segurança
What your team should see in the first 30 days after Cloudflare go-live
The first month should leave your team with tested customer journeys, clear change responsibilities, evidence for tuning decisions, and a usable response record.
Ilyas Esmail
Estratégia de Segurança
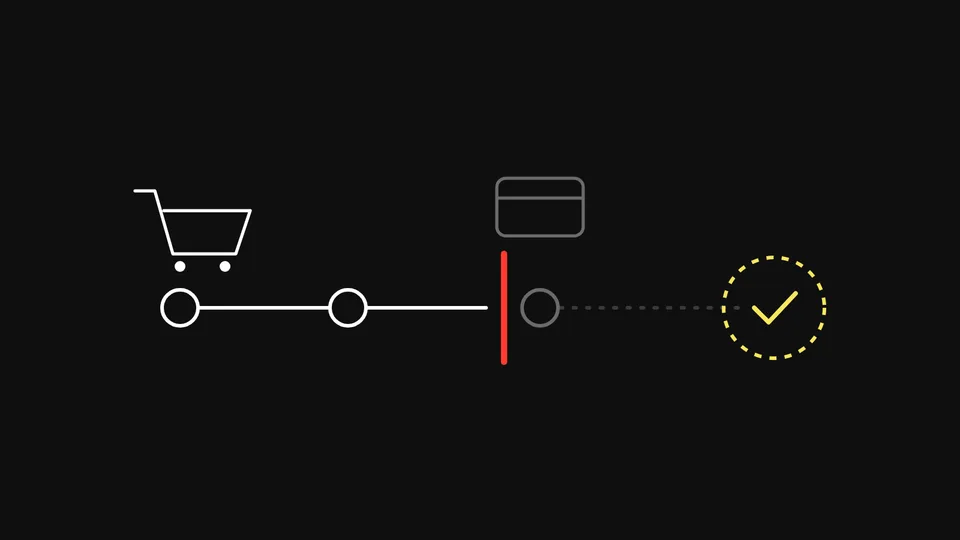
When Cloudflare blocks checkout during your campaign
The campaign is live and support has a blocked-checkout screenshot. Start with the customer journey, connect it to security evidence, and verify the fix through payment.
Ilyas Esmail
Estratégia de Segurança
A Cloudflare WAF change-control runbook for the first hours
A WAF adjustment needs a clear hypothesis, a narrow scope, and a recovery path. Here is what the first hours of a controlled change should contain.
Ilyas Esmail
Estratégia de Segurança
What Cloudflare’s H1 2026 DDoS report means for your edge
Cloudflare is already in front of your application. The next step is making sure your configuration, application changes, and incident response stay aligned.
Ilyas Esmail
Estratégia de Segurança
How banks should choose who runs Cloudflare
For a South African bank, the Cloudflare question is not a partner list. It is who owns WAF, bots, DNS, and Sunday night after go-live.
Ilyas Esmail
Conformidade
Como escolher quem opera a Cloudflare
Uma licença não substitui quem opera a conta. Antes de escolher quem gere a Cloudflare, defina quem vai alterar uma regra WAF numa noite de domingo.
Ilyas Esmail
Estratégia de Segurança
Como os bancos africanos devem contratar a Cloudflare
Os bancos africanos compram frequentemente uma licença Cloudflare e deixam a configuração incompleta. A verdadeira decisão é quem opera a conta após a entrada em produção.
Ilyas Esmail