
Artigos
DestaqueAnúncios
Apresentamos a Vigilbase Network
A Vigilbase passa a operar o AS402630, um passo pequeno mas importante rumo a uma infraestrutura mais fiável e independente.
 Ilyas Esmail
Publicações recentes
Anúncios
The Vigilbase app is on the App Store
Approve changes with Face ID, reply to support, check your sites and ask Vigil about your account, from iPhone, iPad, Mac or Apple Watch. Free for Vigilbase customers.
Ilyas Esmail
Estratégia de Segurança
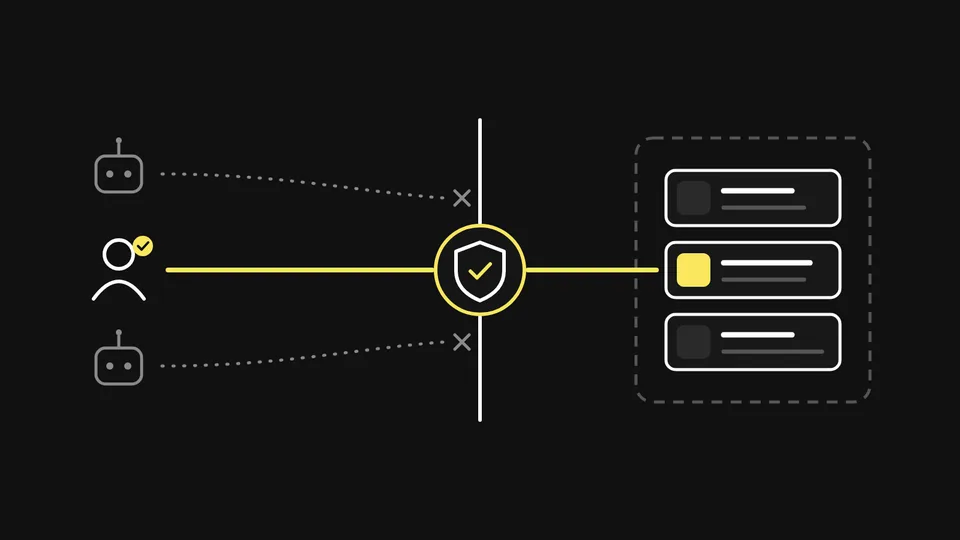
JPMorganChase's CISO is right: your apps shouldn't answer strangers
JPMorganChase's CISO says to stop letting anonymous attackers talk to your systems. What that means in practice, which levers to pull first, and how we run them on Cloudflare One.
Ilyas Esmail
Anúncios
Vigilbase is now in the Claude directory
Ask Claude whether your website is secure, whether someone can spoof your email, what you owe this month or whether anything is down, and get the answer from Vigilbase.
Ilyas Esmail
Estratégia de Segurança
Retail on Cloudflare in 2026, from Singles' Day to the January returns
What Cloudflare managed services for retail should cover in 2026, from the peak-season change freeze to bots, campaign traffic and the scripts on your payment page.
Ilyas Esmail
Ameaças e defesa
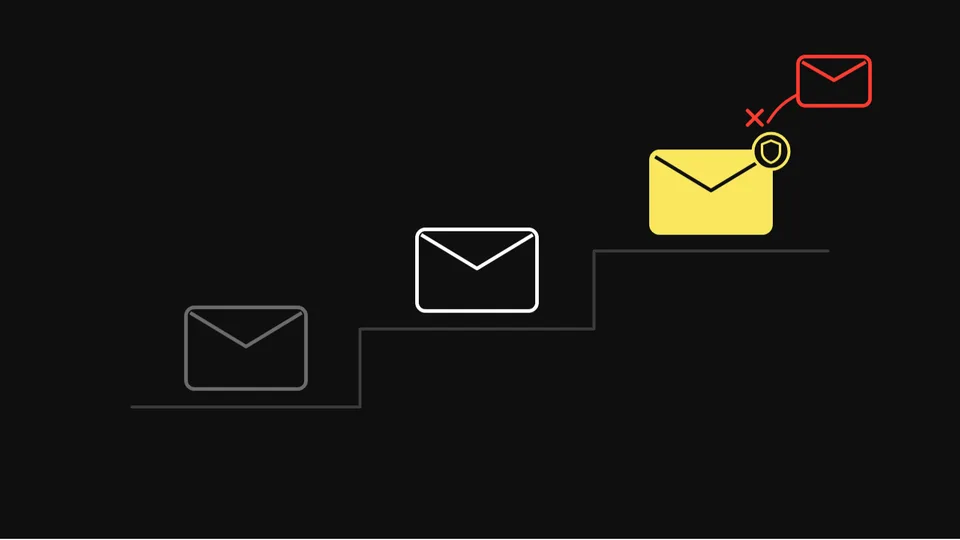
DMARC policy: how to move from p=none to p=reject without losing real email
A DMARC record at p=none satisfies Gmail, Yahoo and Outlook, but it stops nobody spoofing your domain. A staged plan to reach p=reject, with the records to publish at each step.
Ilyas Esmail
Anúncios
Your AI agent can now read the Vigilbase docs
Search and read every page of docs.vigilbase.com from a script or straight from your MCP client, with no account or API key.
Ilyas Esmail
Estratégia de Segurança
Cloudflare can now reach private origins: what it means for your internal apps
Cloudflare can now send proxied traffic to an origin on a private IP over your existing Cloudflare One connection. What changed, who it helps and what to set up first.
Ilyas Esmail
Ameaças e defesa
Cloudflare Under Attack mode: when to turn it on, and what it breaks
Under Attack mode challenges every visitor to your site. It can buy time during an HTTP flood, but it breaks APIs, apps and webhooks. When to use it, how to scope it and what to do first.
Ilyas Esmail
Anúncios
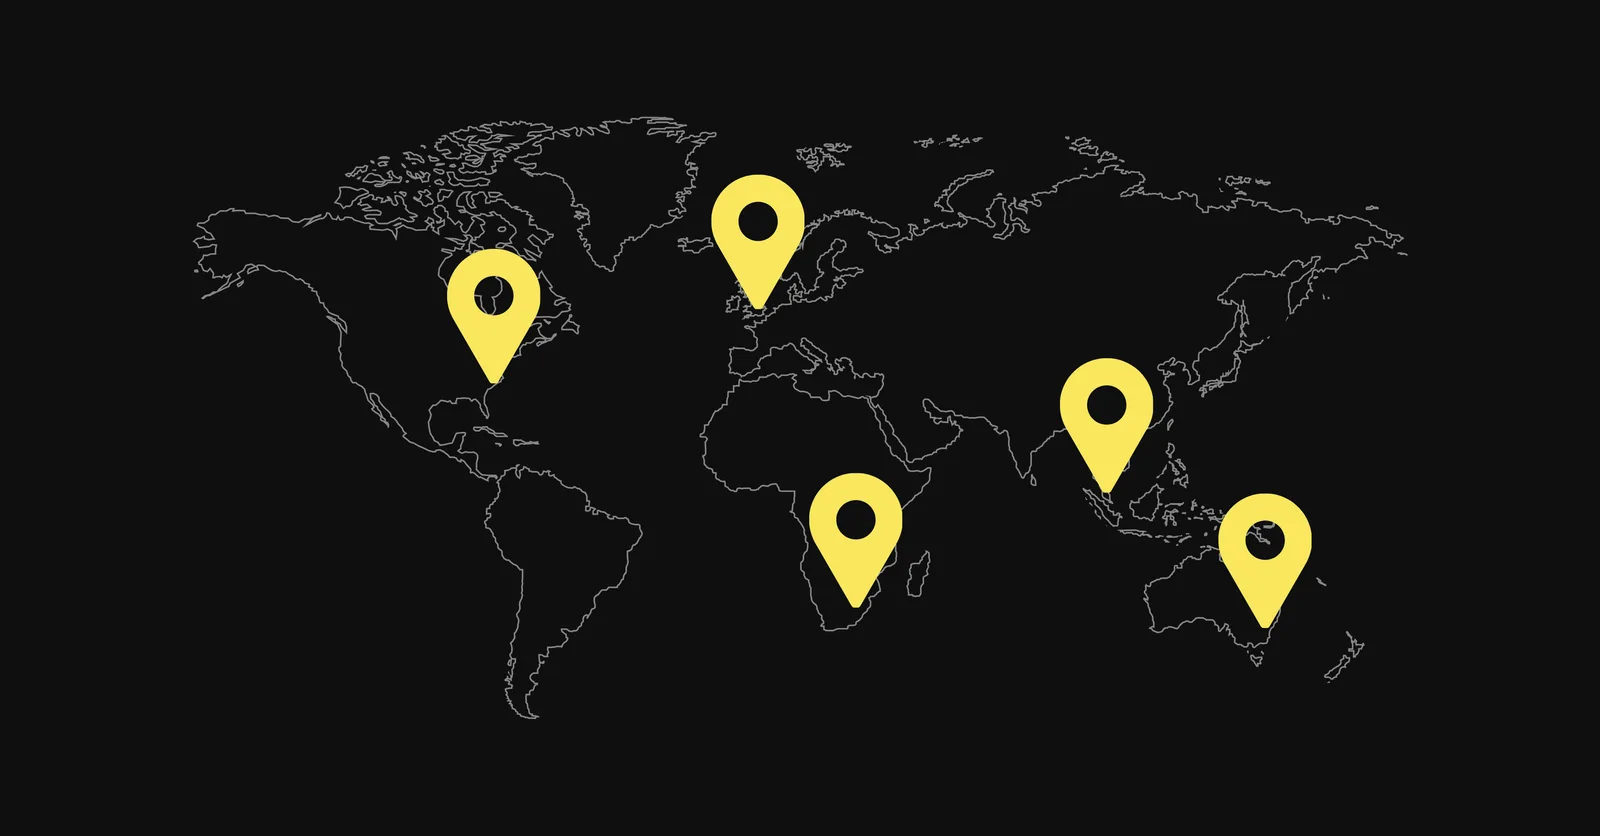
A Vigilbase Network está agora em 29 cidades
O AS402630 está agora em 29 cidades de seis continentes, contra 10. Monitorização mais próxima, failover automático e apenas dois prefixos a autorizar.
Ilyas Esmail
Ameaças e defesa
Security advisory: PHP fixes two critical remote code execution flaws
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical flaws that can allow unauthenticated remote code execution. What is affected, how to check your servers and what to do today.
Ilyas Esmail
Incidentes e Falhas
Security advisory: eight eMudhra CA keys compromised
The private keys of eight eMudhra intermediate CAs can be computed by anyone. Browsers are protected. Servers, containers and API clients may not be. Here is what to check today.
Ilyas Esmail
Ameaças e defesa
Cloudflare rate limiting: the rules to set for login, OTP, API and checkout
Which Cloudflare rate limiting rules to write first, what each plan allows, and how to set thresholds that stop credential stuffing without locking out customers behind shared IPs.
Ilyas Esmail
Estratégia de Segurança
What your team should see in the first 30 days after Cloudflare go-live
The first month should leave your team with tested customer journeys, clear change responsibilities, evidence for tuning decisions, and a usable response record.
Ilyas Esmail
Estratégia de Segurança
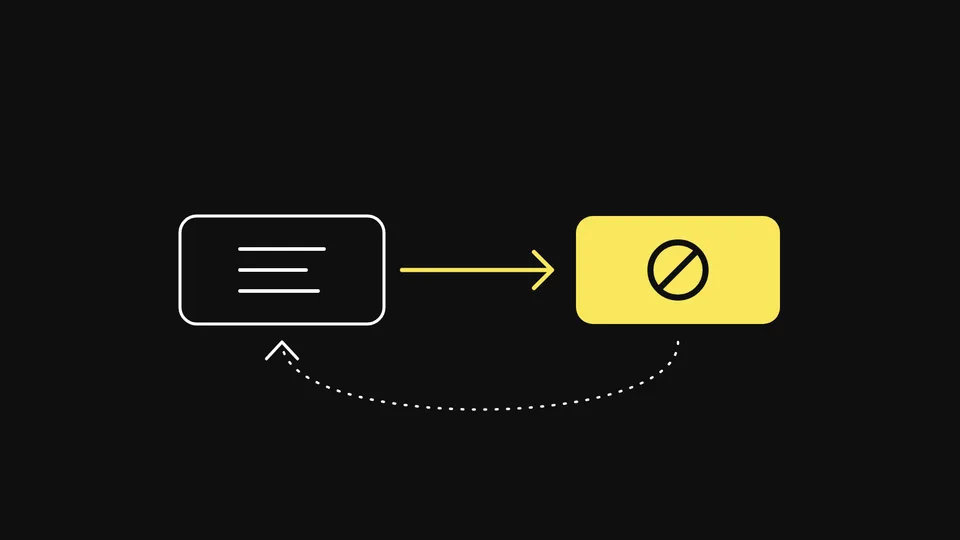
When Cloudflare blocks checkout during your campaign
The campaign is live and support has a blocked-checkout screenshot. Start with the customer journey, connect it to security evidence, and verify the fix through payment.
Ilyas Esmail
Estratégia de Segurança
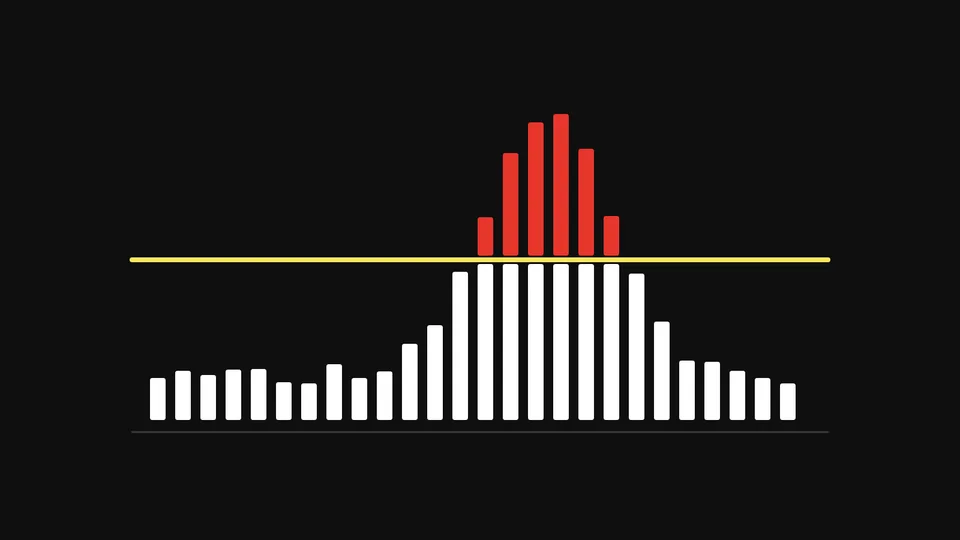
A Cloudflare WAF change-control runbook for the first hours
A WAF adjustment needs a clear hypothesis, a narrow scope, and a recovery path. Here is what the first hours of a controlled change should contain.
Ilyas Esmail
Estratégia de Segurança
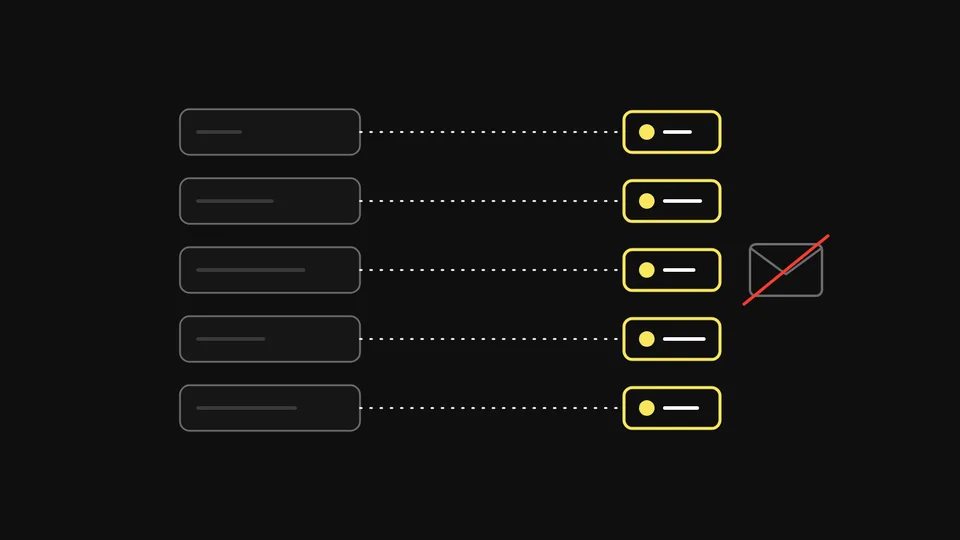
What Cloudflare’s H1 2026 DDoS report means for your edge
Cloudflare is already in front of your application. The next step is making sure your configuration, application changes, and incident response stay aligned.
Ilyas Esmail
Estratégia de Segurança
How banks should choose who runs Cloudflare
For a South African bank, the Cloudflare question is not a partner list. It is who owns WAF, bots, DNS, and Sunday night after go-live.
Ilyas Esmail
Conformidade
Como escolher quem opera a Cloudflare
Uma licença não substitui quem opera a conta. Antes de escolher quem gere a Cloudflare, defina quem vai alterar uma regra WAF numa noite de domingo.
Ilyas Esmail
Estratégia de Segurança
Como os bancos africanos devem contratar a Cloudflare
Os bancos africanos compram frequentemente uma licença Cloudflare e deixam a configuração incompleta. A verdadeira decisão é quem opera a conta após a entrada em produção.
Ilyas Esmail
Anúncios
Artigo histórico
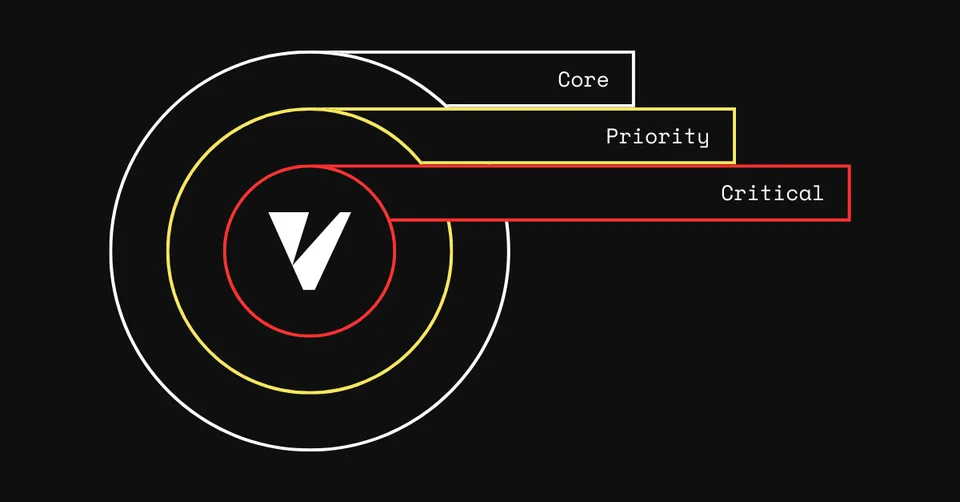
Apresentamos os Níveis de SLA Unificados: Core, Priority e Critical
O anúncio dos níveis de serviço em dezembro de 2025. Consulte o SLA atual para conhecer o âmbito e a cobertura dos pacotes Vigilbase.
Ilyas Esmail
Incidentes e Falhas
Falha da Cloudflare a 18 de novembro de 2025
A Vigilbase detetou precocemente a falha da Cloudflare, ajudou os clientes a manterem-se online e está a implementar automação para evitar impactos futuros.
Ilyas Esmail
Fique atualizado
Receba os mais recentes insights sobre cibersegurança na sua caixa de entrada.